Skip to content

Sample Report: Web & API Penetration Test

About 30 pages · German or English · PDF


The fictional Heveon GmbH runs a self-service portal through which around 40 Swiss SMEs manage payslips, IBANs and social insurance numbers of their employees. Before go-live, we tested the web application and the REST API as a grey-box assessment over eight business days. The report documents six vulnerabilities, one of them critical, each with proof, risk rating and concrete remediation.
Email me the report

A look inside the report


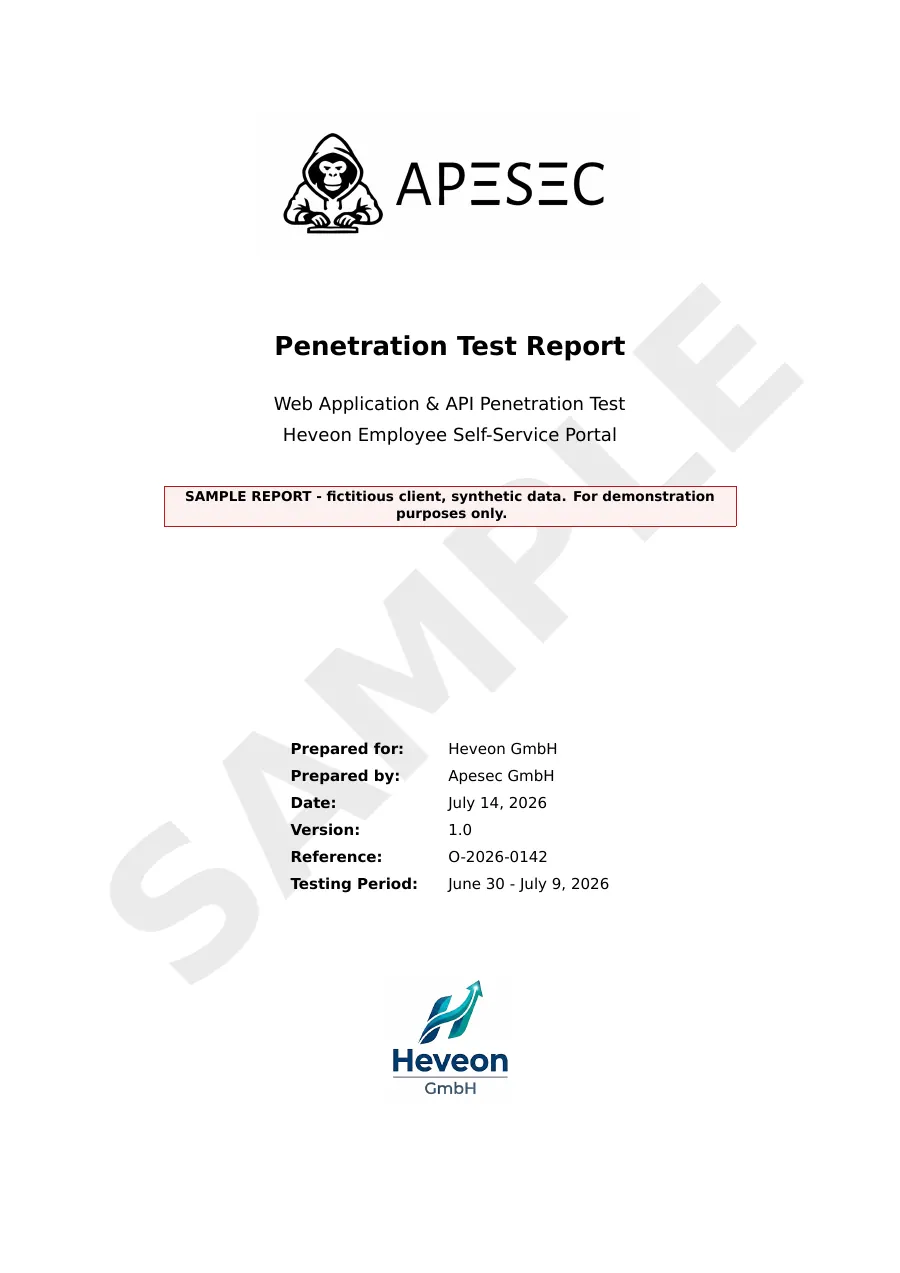
Cover page of the sample report
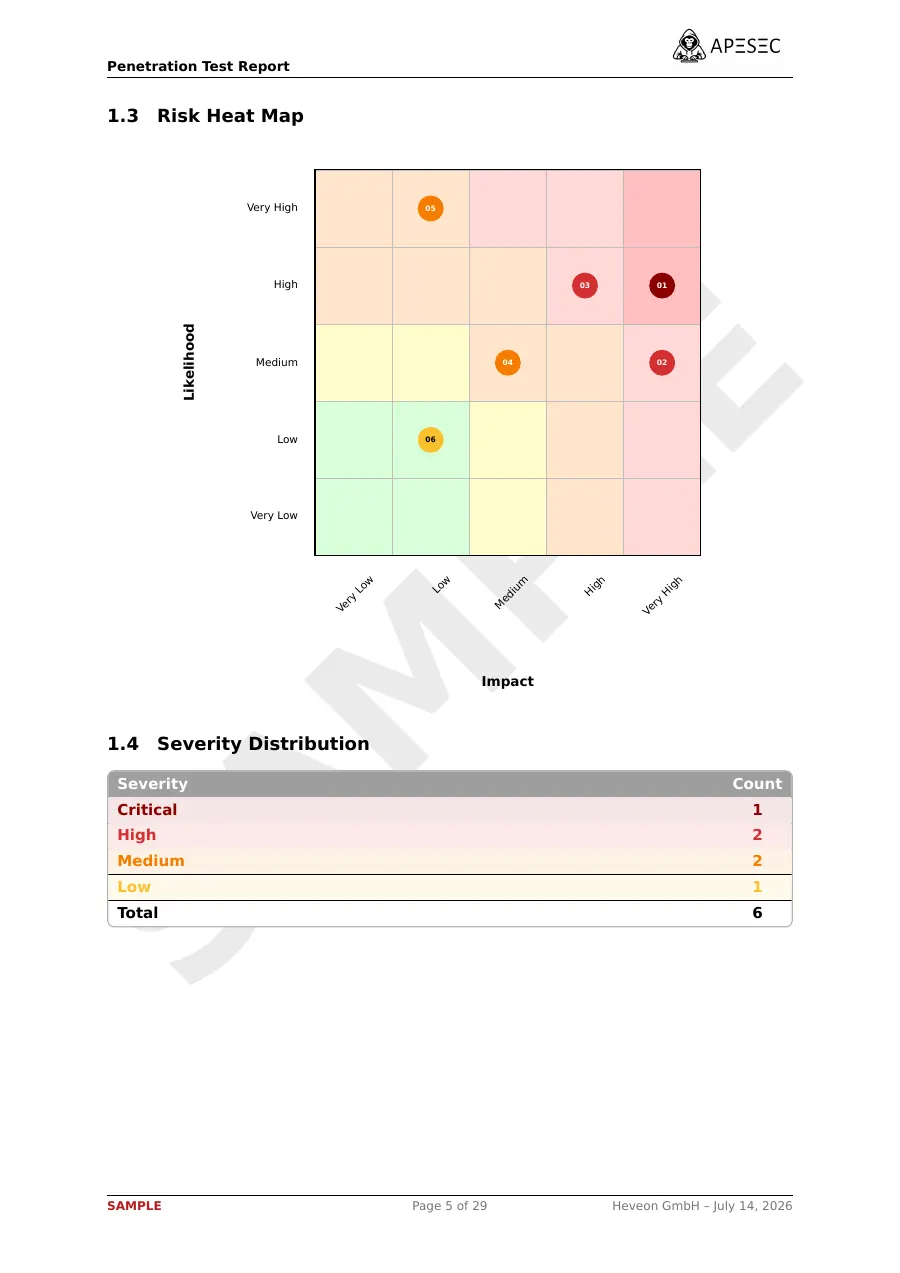
Risk heat map and severity distribution
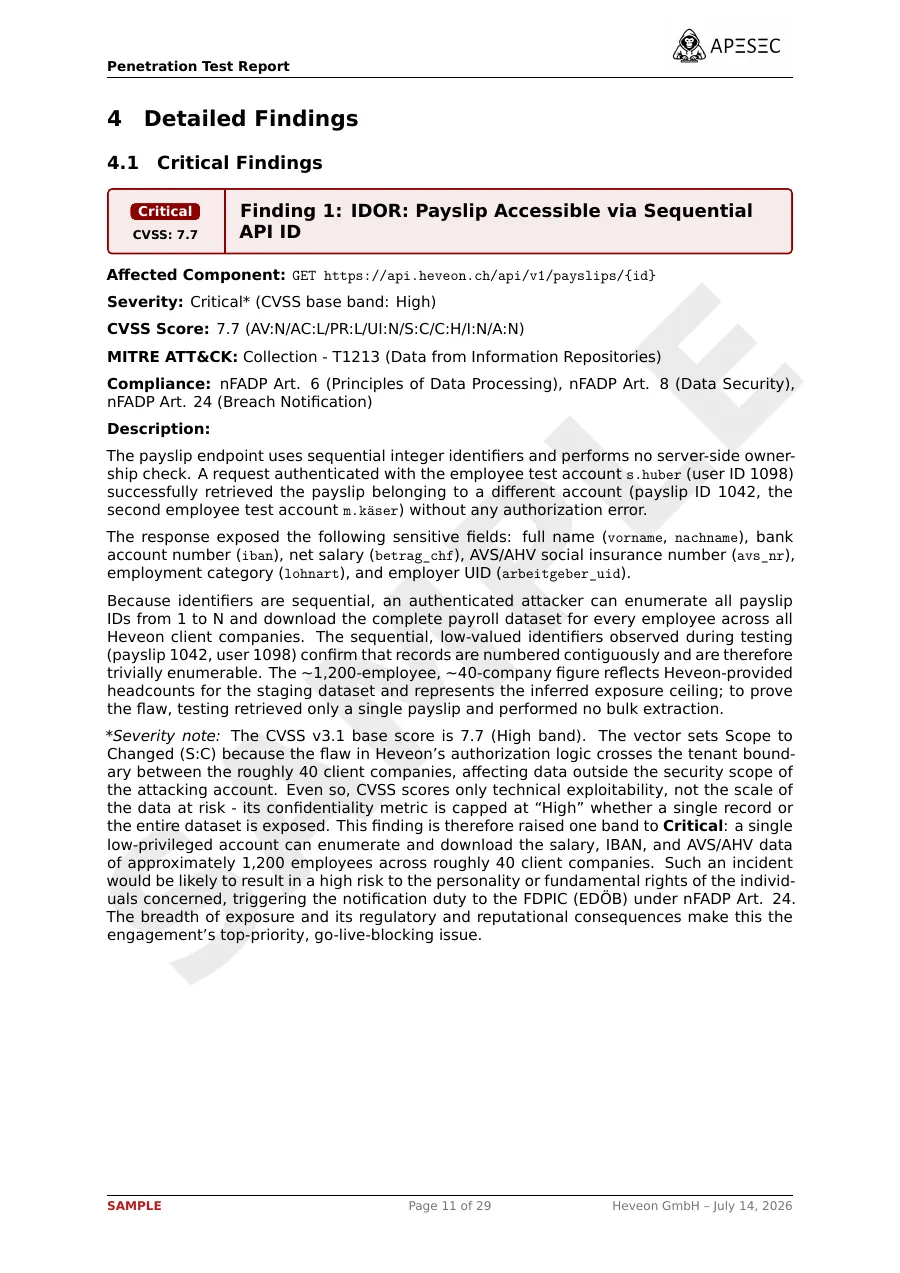
Finding 1: IDOR with proof of concept

What the report contains


The findings at a glance

# Finding Severity
1 IDOR: Payslip Accessible via Sequential API ID Critical
2 Broken Authentication: Password-Reset Token Reusable After Use High
3 Business Logic: Expense Amount Client-Controlled High
4 Sensitive Data in JWT Payload Medium
5 Legacy API v0 Admin Endpoint Still Reachable Medium
6 Missing HTTP Security Headers Low

The client, people and data in the report are fictional. The vulnerabilities and evidence come from a test environment built for this purpose.

Get the report by email, free of charge


Which reports would you like?

We use your details to send you the report. You will only receive further emails if you tick the box above. More in our privacy policy.

Another sample report


Sample report: Internal pentest

From a standard account to Domain Admin: 33 pages with nine findings, proof and a remediation roadmap. Free by email.

View sample report