Skip to content

Sample Report: Internal Network and Active Directory Pentest

33 pages · German or English · PDF


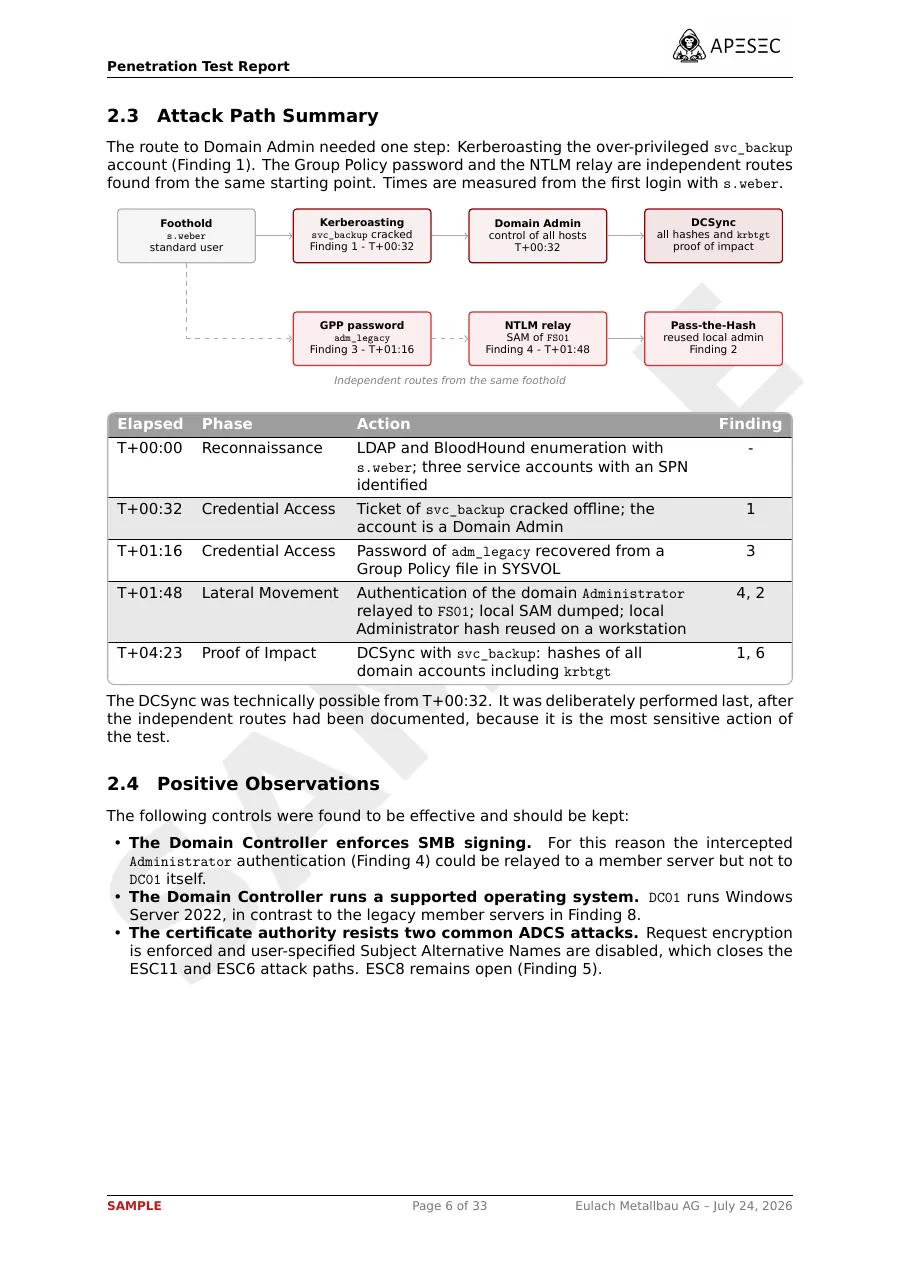
Starting point: an attacker knows the password of a single employee account, for example after a phishing email. How far do they get in the network of the fictional Eulach Metallbau AG, and how fast? Starting from a standard account without special rights, we gained full control of the Active Directory domain within 32 minutes. The report documents the attack path and nine findings, each with proof, risk rating and concrete remediation.
Email me the report

A look inside the report


Cover page of the sample report
Attack path to Domain Admin with timeline
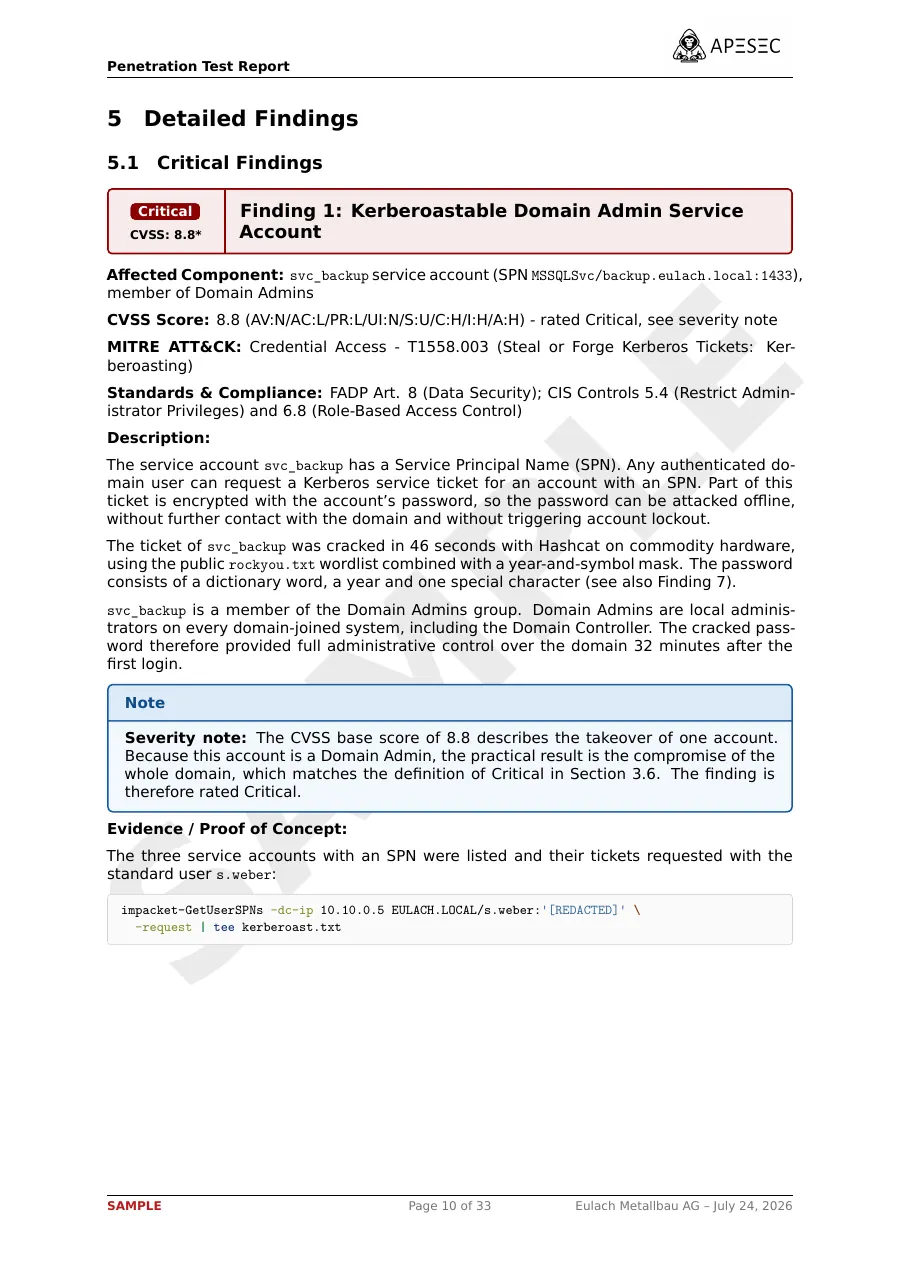
Finding 1: Kerberoasting with proof of concept

What the report contains


The findings at a glance

# Finding Severity
1 Kerberoastable Domain Admin Service Account Critical
2 Shared Local Administrator Password (No LAPS) High
3 Recoverable Password in SYSVOL (GPP cpassword) High
4 NTLM Relay: SMB Signing Not Enforced High
5 ADCS ESC8: Web Enrollment Without Extended Protection High
6 Explicit Directory-Replication Rights on a Service Account High
7 Predictable Passwords on User and Service Accounts Medium
8 Windows Server 2012 R2 (End-of-Life) Medium
9 Anonymous LDAP Queries Permitted Medium

The client, people and data in the report are fictional. The vulnerabilities and evidence come from a test environment built for this purpose.

Get the report by email, free of charge


Which reports would you like?

We use your details to send you the report. You will only receive further emails if you tick the box above. More in our privacy policy.

Another sample report


Sample report: Web & API pentest

About 30 pages with six findings, proof, risk ratings and a remediation roadmap. Free by email.

View sample report